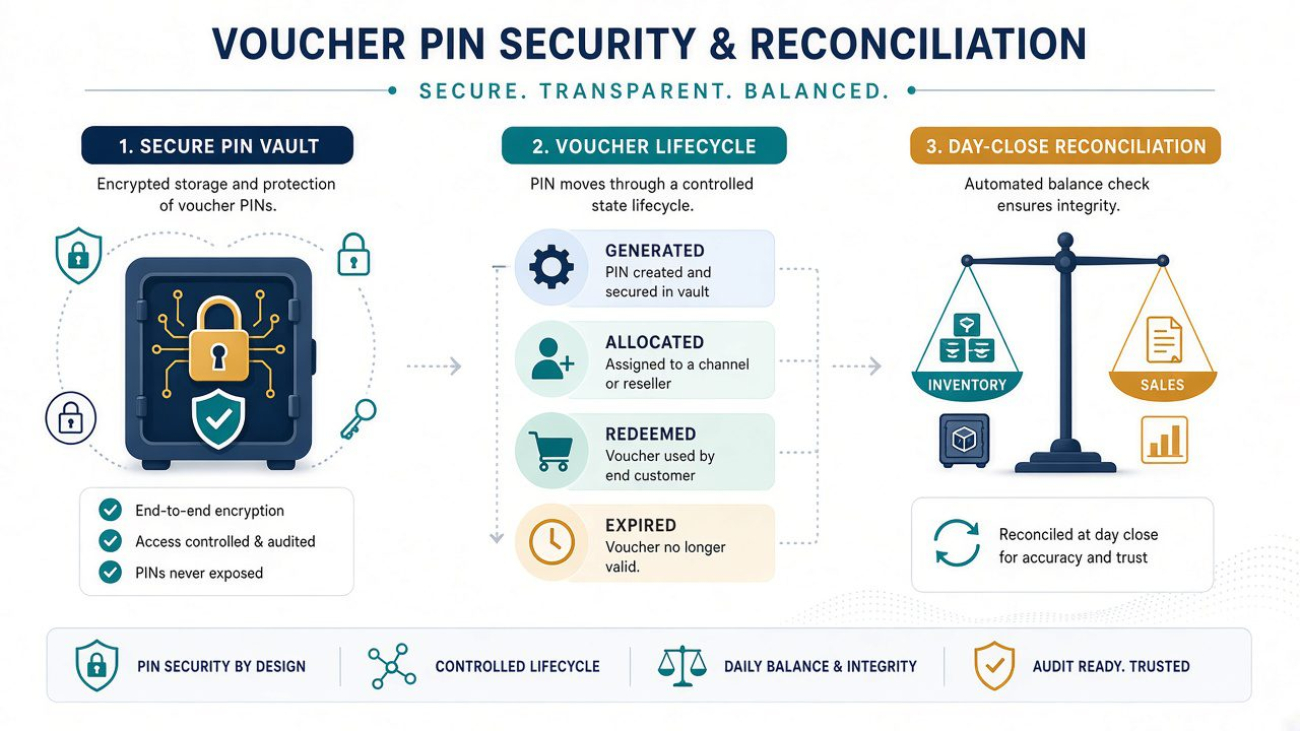
Voucher reconciliation is the day-close discipline that proves prepaid inventory, channel sales, and charging redemptions tell the same story. In an electronic voucher management system, that discipline sits beside PIN security: encryption of voucher secrets, controlled lifecycle states, custody rules, and audit trails that survive operator review. Buyers evaluating EVMS platforms should treat security and reconcile as one operating problemnot two slide decks.
TL;DR
- PIN security without reconcile still leaves finance arguing with fraud; reconcile without PIN custody still leaks value at the edges.
- Lifecycle states (generated allocated sold redeemed / expired / cancelled) are the spine of both inventory control and audit.
- Physical theft and damage matter less when secrets never sit as plain text; float misuse and insider reveal become the primary risks.
- Inventory-vs-sales and sales-vs-charging packs need named owners for exceptionsor disputes never close.
- For platform scope beyond security alone, see the electronic voucher management system overview.
Why PIN security and reconciliation belong in the same brief
Telecom prepaid looks simple from the shop floor: sell value, credit a phone. Inside the stack, two failure modes dominate steering-committee conversations.
First, secrets leak. A batch file emailed unencrypted, a POS that caches clear PINs, a reprint without dual controleach becomes an unauthorised redemption somewhere else in the network.
Second, numbers disagree. Dealer wallets show one total; POS reports another; charging redemptions land somewhere in between. Without voucher reconciliation, every mismatch becomes a blame loop among channel ops, finance, and the vendor.
An electronic voucher management system earns its keep when it shrinks both failure modes with the same data model: serialised stock, status gates, encrypted secrets, and transaction ids that finance can follow end to end.
Industry and standards writing reinforce the pattern. Payment and voucher programmes commonly require unique end-to-end identifiers, encrypted storage of sensitive voucher data, and internal/external reconciliation across partiessee, for example, GovStacks voucher and payment orchestration requirements on voucher storage, audit, and reconciliation. Separately, GSMA work on airtime distribution economics shows why operators care about electronic channels in the first place: reducing scratch-card manufacturing and channel costs only sticks if the digital path is trustworthy (GSMA on airtime distribution savings).
PIN security: what encrypted until sale really means
Buyers hear PINs are encrypted in every demo. Ask what that covers.
At rest
Voucher secrets should not live as readable columns in a spreadsheet extract or an unprotected database dump. Encryption at rest, key custody separate from application admins where feasible, and segregation of duties for who can decrypt or export are the baseline questions. If a developer can pull a CSV of live PINs from production with one ticket, you do not have PIN securityyou have theatre.
In transit
Channels that reveal or transmit PINs (print-on-demand, SMS delivery, POS display) need TLS and channel authentication. Reveal should be tied to an authorised sale event, not a casual preview.
At reveal
The moment of sale is the highest-risk second. Controls that matter:
- Role and device authentication before reveal.
- One-time reveal logging (who, which terminal, which batch, which MSISDN if applicable).
- Reprint / re-reveal policies with dual control and reason codes.
- Velocity limits so a compromised retailer cannot drain a batch overnight.
Against guessing and replay
PIN and voucher number schemes should resist trivial prediction. Redemption paths need duplicate and replay protection so the same secret cannot credit twice. Timeout handling must be explicit: did charging accept, or do we leave the voucher in a pending-investigation state?
None of this requires inventing exotic cryptography for a blog post. It requires operational honesty about who can see secrets and how redemptions are proven.
Lifecycle states: the shared language of ops and audit
Thin EVD tools skip states. Serious EVMS designs make them unavoidable:
| State | Meaning | Typical controls |
|---|---|---|
| Generated / intake | Batch created or imported under policy | Batch metadata, denomination, expiry, encryption plugin |
| Available | Eligible for allocation | Not yet assigned to a channel node |
| Allocated | Assigned to distributor / dealer / wallet | Hierarchy transfer rules, credit limits |
| Sold / issued | Revealed or committed to a sale | Float debit, reveal log, channel id |
| Redeemed | Charging accepted credit | Unique redemption id, duplicate block |
| Expired | Past validity | Reporting and write-off policy |
| Cancelled / blacklisted | Removed from sale (theft, error, fraud) | Batch or serial block, audit reason |
| Pending / exception | Ambiguous after timeout or partial failure | Human queue with owner |
Every transition should leave an audit trail. If someone can silently move a serial from available to sold without a transaction, reconcile will never close.
For distribution context around how stock moves through resellers, see What is electronic voucher distribution (EVD)?.
Theft, damage, and the shift in risk profile
Physical scratch programmes lose value to damaged cards, wet cartons, and outright theft in transit. Electronic programmes reduce those modesthen invent new ones:
- Insider reveal Staff or partners exporting batches.
- Terminal compromise Lost POS still authorised to sell.
- Social engineering Fake support asking for reprints.
- Float gaming Collusion between hierarchy nodes and fake sales/reversals.
- Charging mismatch exploits Selling when redemption is known flaky, then disputing.
Mitigations are operational: device disablement, short-lived sessions, dual control on sensitive actions, batch blacklist playbooks, and reconcile packs that surface anomalies early. We went digital is not a control. Digital without custody is just faster leakage.
Inventory vs sales vs charging: three ledgers, one close
Voucher reconciliation usually means matching three views:
- Inventory ledger What serials exist in which state, by batch and hierarchy node.
- Sales ledger What the channel claims it sold (POS, USSD, API, portal).
- Charging / redemption ledger What the IN/OCS or voucher redeem service accepted.
Healthy day-close asks:
- Opening available + allocations sales cancels expiries = closing available?
- Sales by dealer float debits for that dealer?
- Sold PIN serials that should redeem successful redemptions (with timing lag understood)?
- Exceptions queued with owners and age SLAs?
When sales and charging disagree, you do not adjust in Excel and move on. You open an exception with a reason class: timeout, double-submit, charging reject after local commit, channel clock skew, or suspected fraud. Platforms that cannot classify exceptions force humans to invent folklore.
Checklist: security + reconcile readiness
Use this in RFPs and discovery workshops:
| Area | Ask / prove |
|---|---|
| Secrets | Encryption at rest; no clear PIN in routine exports |
| Keys | Who holds keys; rotation; segregation from app admins |
| Reveal | Sale-gated reveal; reprint dual control; full reveal log |
| Lifecycle | Explicit states; illegal transitions blocked |
| Audit | Immutable (or WORM-style) logs for privileged actions |
| Ids | Unique end-to-end transaction ids across sale and redeem |
| Reconcile pack | Daily inventory, sales, float, redemption, exceptions |
| Ownership | Named queues for finance, fraud, and channel ops |
| Devices | Loss/disable workflow; version inventory |
| Hybrid | Physical + electronic under one status model if both exist |
If a vendor can only demo generate PIN show on phone, keep looking. That line exists on the product page for a reason.
How EVD System frames the problem
EVD System by MoboGage is built as the prepaid control plane: generation or intake, hierarchy allocation, multi-channel sale, redemption path, and reconciliation finance can use. PIN custody and day-close are not add-on slogans; they are why operators and VAS partners adopt an EVMS instead of a thin top-up widget.
When you compare vendors, How to choose an electronic voucher management system outlines evaluation axesincluding security review posture and reconciliation packs that work on a normal day, not only in a scripted demo.
Soft next step
Pick one recent week of prepaid exceptions. Count how many were numbers dont match versus PIN may have leaked. That split usually tells you whether to prioritise reconcile tooling, custody hardening, or both before you argue about UI themes.
For a structured conversation about EVD System, see About MoboGage or the contact page projects@mobogage.com +91-9928 366 889.
FAQ
What is voucher reconciliation in telecom prepaid?
It is the process of matching inventory states, channel sales (and float movements), and charging redemptions so finance and fraud can close the day with known exceptionsnot unexplained gaps.
How does PIN security relate to an electronic voucher management system?
An EVMS governs voucher secrets across their lifecycle. PIN security is the set of encryption, access, reveal, and redemption controls that keep those secrets from becoming unauthorised credit.
Can we reconcile if we only run PINless eTopup?
Yesbut the objects change. You reconcile float and sales against charging credits more than serial PIN states. Many operators still want EVMS-grade audit when any PIN products remain in the catalog.
What should a day-close pack include?
Opening/closing inventory or float, sales by channel and dealer, redemptions, cancels/expiries, and an aged exception list with owners and reason codes.
How do we handle a compromised batch?
Blacklist or cancel affected serials, notify channel nodes, preserve audit evidence, and reconcile remaining inventory immediately. Document the playbook before you need it at 2 a.m.
Is encryption alone enough?
No. Encryption without role control, reveal policy, device hygiene, and reconcile ownership still fails in ordinary operations.